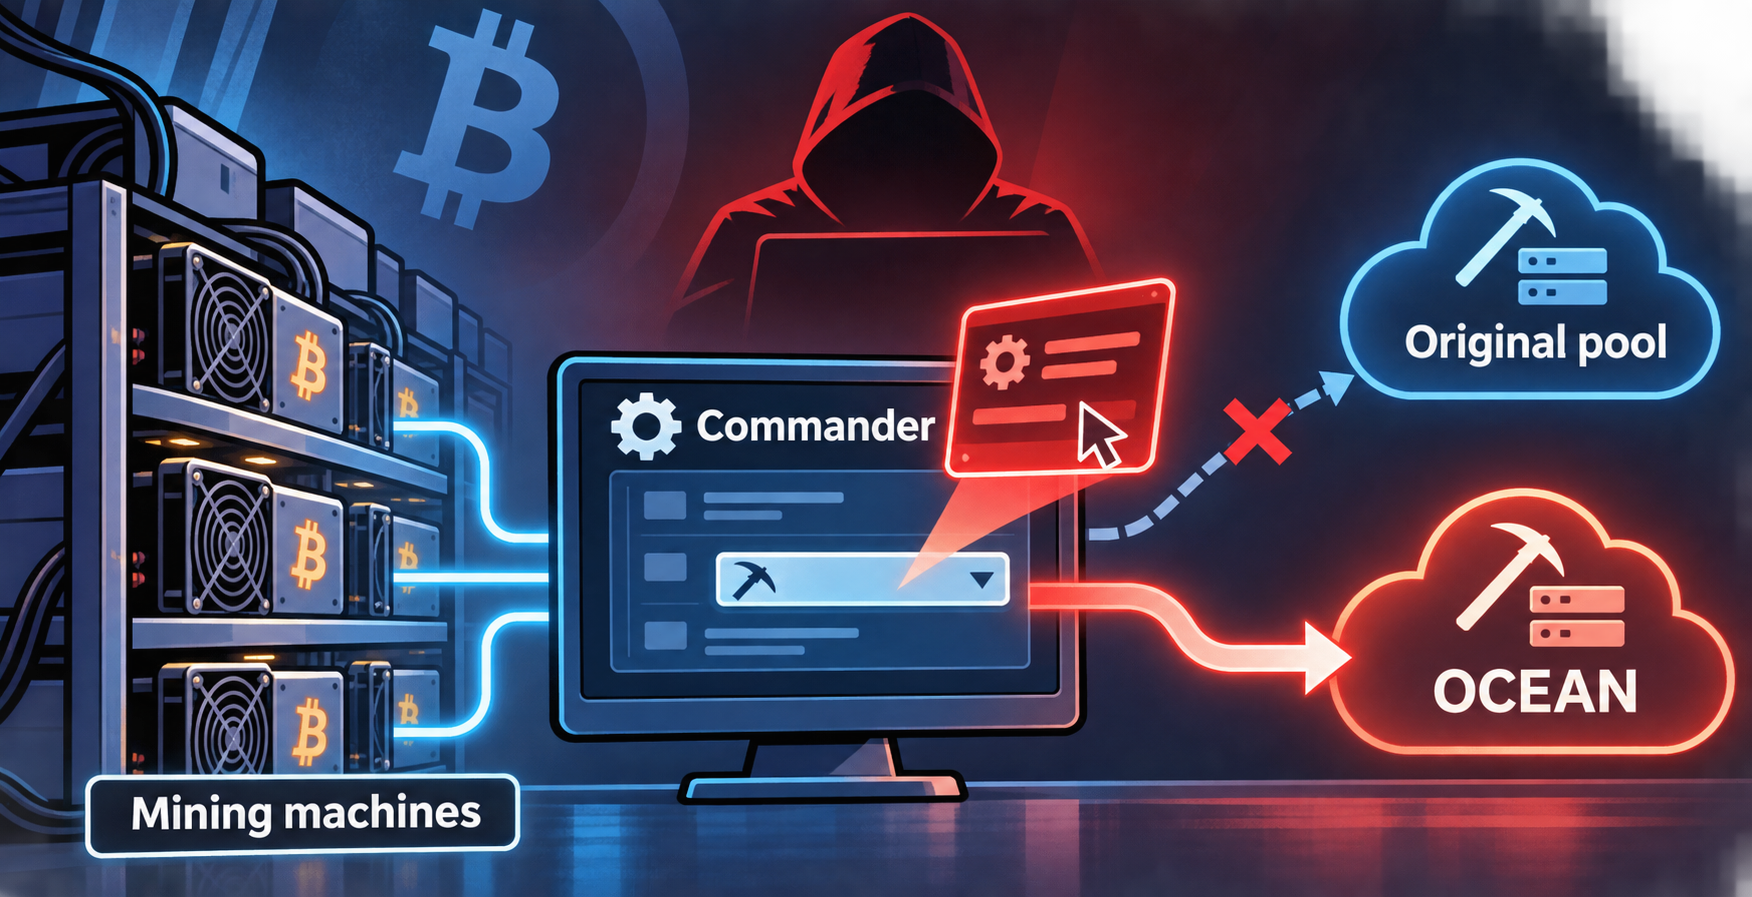
What happens when someone changes a miner’s pool settings without authorization? In a report published on November 16, 2026, at 10:33 UTC+8, Cointelegraph said attackers had compromised Luxor’s Commander mining-management tool and redirected computing power from affected customers to the OCEAN mining pool over the preceding weekend.
Initial reports put the diversion at roughly 64,000 machines and 13 exahashes per second (EH/s). Luxor did not confirm those figures. It said just over a dozen customer accounts using Commander were affected, and that its Luxor Pool and LuxOS services were not affected.
Luxor said it patched Commander within two hours of detecting the unauthorized changes and began restoring machines to their original pool settings. It pledged to compensate customers in full for the redirected mining power and to publish a post-mortem. The source does not provide the affected customers’ individual hashrates, the duration of each diversion or a compensation calculation.
Initial reports suggested the attackers received no mining rewards. Separately, CoreX identified a Bitcoin address as associated with the incident; that address subsequently received two OCEAN payouts totaling approximately 0.162 BTC, worth about $10,500 at the value reported by Cointelegraph. The source does not establish who controlled the address.
Luxor CEO Nick Hansen called the intrusion a “sophisticated AI-enabled” attack but did not specify how AI was used. He said Luxor had put most feature work on hold to strengthen cybersecurity and acquired GPUs to run open-weight AI models for security work. Those are Hansen’s account of the company’s response, not evidence of a disclosed attack method.
Source: cointelegraph.com (originally published 2026-11-16 10:33 UTC+8)