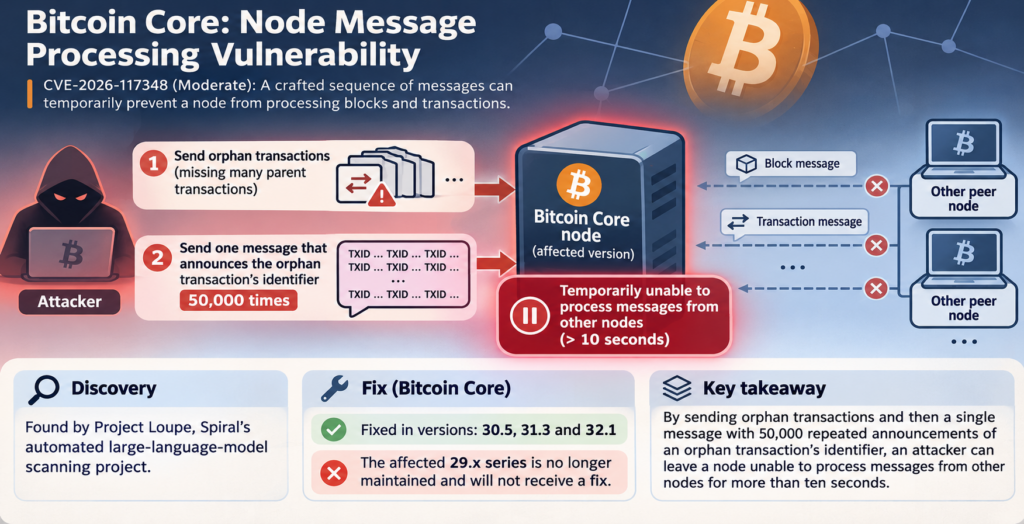
Could a single message delay a Bitcoin node from processing messages sent by other nodes? In a report dated November 21, 2026, Bitcoin Core disclosed a moderate-severity vulnerability, CVE-2026-117348, that could temporarily prevent a node from processing blocks and transactions.
An attacker could first send orphan transactions missing many parent transactions, then announce an orphan transaction’s identifier 50,000 times in one message. According to the disclosure, this could leave the node unable to process messages from other nodes for more than ten seconds.
The vulnerability was found by Project Loupe, Spiral’s automated large-language-model scanning project. Bitcoin Core versions 30.5, 31.3 and 32.1 include a fix. The affected 29.x series is no longer maintained and will not receive one.