How much mining capacity was redirected, and for how long? In reporting published November 16, 2026, Luxor Technology said an attack on its Commander fleet-management software had redirected hashrate from more than a dozen client accounts to another mining pool over the preceding weekend. Luxor described the attack as AI-enabled.
Luxor said it detected the unauthorized redirects on Saturday. Its on-call engineers patched the vulnerability within two hours and began restoring affected machines to their original pool settings. The company said no data was leaked or exfiltrated, the issue was limited to Commander, and its other services were unaffected. It said Commander was operating normally and users needed to take no further action.
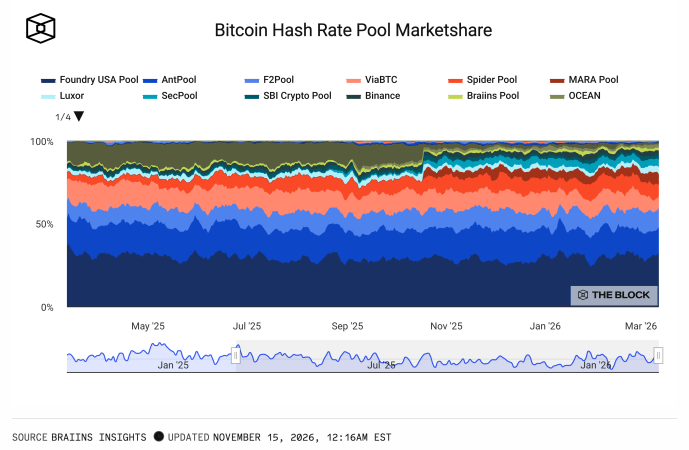
Luxor CEO Nick Hansen told The Block the affected hashrate was about 13 EH, which he valued at approximately $20,000 per hour. That is Hansen’s estimate of the redirected hashrate’s hourly value, not a reported total loss. Luxor said it planned to fully compensate affected clients. The report did not state a final compensation amount.
The incident followed Luxor’s announcement in September 2026 of Luxor AI, an expansion into AI and high-performance computing. The company also raised $16 million in a strategic funding round the following month. Neither development establishes how the Commander attack occurred.