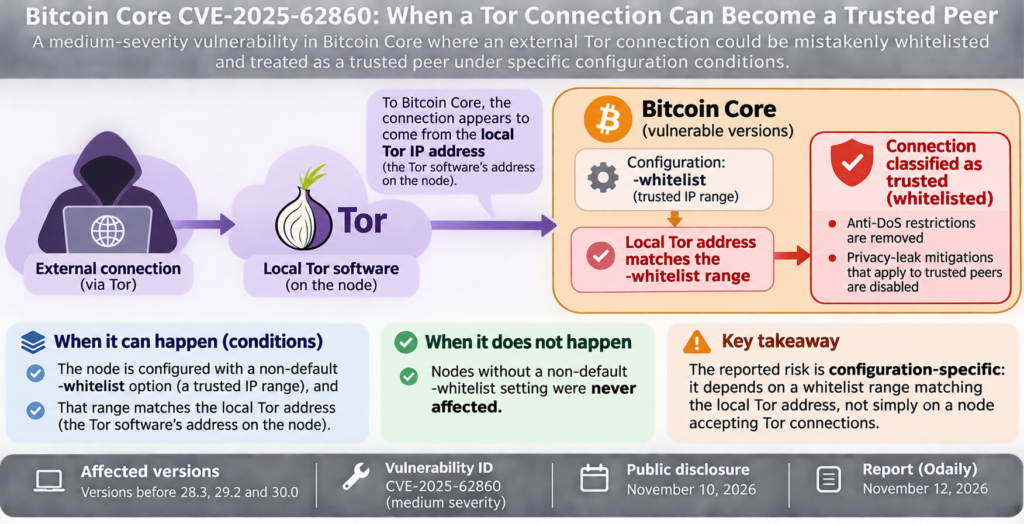
Could an external Tor connection be treated as a trusted Bitcoin Core peer? In a report published on November 12, 2026, Odaily described a medium-severity Bitcoin Core vulnerability, CVE-2025-62860, that had been publicly disclosed on November 10.
The issue affected versions before 28.3, 29.2 and 30.0. An external connection arriving through Tor appeared to Bitcoin Core to have the IP address of the local Tor software. If that address matched a trusted IP range set with the -whitelist option, Bitcoin Core could mistakenly whitelist the external connection. That would remove anti-denial-of-service restrictions and privacy-leak mitigations that apply to trusted peers.
According to the disclosure, nodes without a non-default -whitelist setting were never affected. The distinction is configuration-specific: the reported risk depended on a whitelist range matching the local Tor address, not simply on a node accepting Tor connections.